Newsletter Subscribe
Enter your email address below and subscribe to our newsletter
Enter your email address below and subscribe to our newsletter
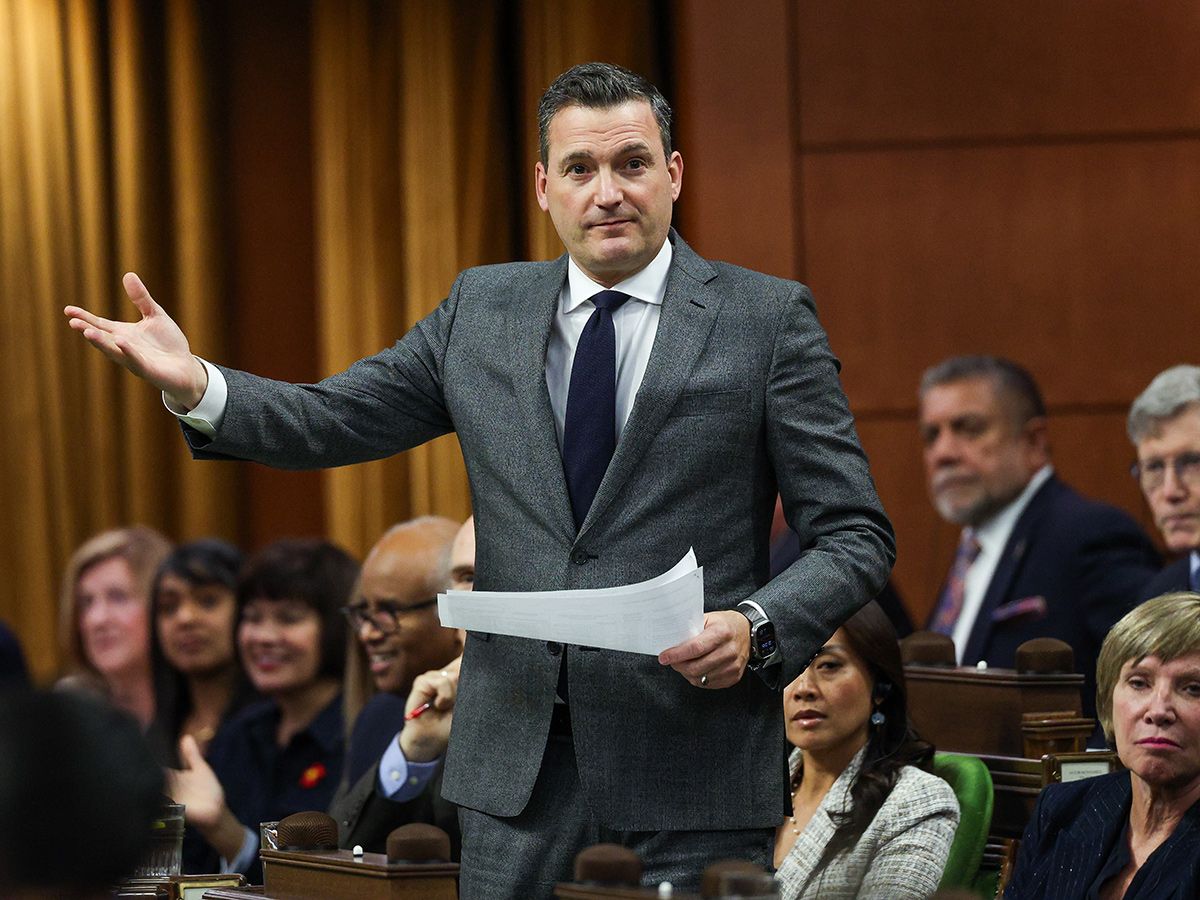
OTTAWA — Multiple Government of Canada websites were pulled offline for “urgent maintenance” after two major cybersecurity flaws were discovered in a programming language that underpins the majority of web pages around the world.
On Wednesday, Artificial Intelligence Minister Evan Solomo n confirmed that the government had pulled an undisclosed number of its websites temporarily to patch the vulnerabilities revealed earlier in the day. The “critical” flaws were discovered in PHP, a popular programming language that supports a “substantial” proportion of websites across the world.
“Some Government of Canada websites have been temporarily taken offline as a precaution to protect government systems and Canadians’ information, following guidance from the Canadian Centre for Cyber Security,” Solomon said.
He encouraged all Canadian website owners who also use impacted PHP websites to install fixes immediately.
On Wednesday, PHP issued an advisory as well as patches to two major cyber vulnerabilities that were sitting in its software code for years and were recently discovered by artificial intelligence.
According to various cybersecurity agencies worldwide, the flaws could allow hackers virtually unfettered access to an affected web server’s file system or databases.
PHP’s advisory left network defenders scrambling to either take their systems offline or develop a fix of their own until PHP released its own patches a few hours later. But the effects — and potential intrusions — caused by the major vulnerabilities likely won’t be discovered by impacted organizations for days or weeks.
Canada’s warning to quickly patch the two flaws discovered by PHP echoes stark advisories issued by European, American and Asian government agencies, underscoring how the critical the newly-discovered vulnerabilities truly are.
The website for the department of Industry, Science and Economic Development (ISED) appeared to be one affected by the vulnerability. On Wednesday, the department’s homepage displayed an error and told users that the “service is temporarily offline while we carry out urgent maintenance.”
Queries to ISED and the Canadian Centre for Cyber Security (CCCS) were redirected to the Treasury Board Secretariat, which did not immediately respond to a request for comment.
The CCCS joined international partners such as the United States National Security Agency in calling on all owners of websites using certain versions of PHP to patch their websites immediately or risk an intrusion by cyber threat actors.
The U.S. agency’s warning was extremely direct: patch your system immediately or take your website offline for the time being.
In its advisory, the CCCS also noted it had seen reports of evidence that the vulnerabilities could be exploited by criminal actors, but that there is “no active exploitation being identified at this time,” though “that can change quickly.”
Experts said that the vulnerabilities would have been extremely difficult for hackers to discover previously, but AI has since exponentially reduced the speed at which such issues are discovered.
Ramy Rahman, a senior engineer at U.S.-based cybersecurity firm ArmorCode, said in a release that AI now gives network defenders far less time to guard themselves when a new vulnerability is discovered.
“AI makes it easier to examine large amounts of code and revisit flaws previously considered too difficult to exploit. It also helps attackers reverse-engineer patches, shortening the window between a fix becoming public and an exploit becoming available,” Rahman wrote.
“Flaws we once thought were impractical to exploit are back on the table. The underlying risks aren’t new, but exploiting them is becoming easier and accessible to more people. We need to revisit old assumptions and get faster at patching.”
National Post
cnardi@postmedia.com
Our website is the place for the latest breaking news, exclusive scoops, longreads and provocative commentary. Please bookmark nationalpost.com and sign up for our newsletters here.